
WASHINGTON — Sen. Elizabeth Warren is calling on three federal banking regulators to reverse changes to supervisory policies that she says could prevent examiners from addressing cybersecurity risks as artificial intelligence makes cyberattacks more sophisticated.
Warren (D-MA), the ranking Democrat on the Senate Banking Committee, sent letters Friday to Federal Reserve Vice Chair for Supervision Michelle Bowman, Comptroller of the Currency Jonathan Gould and Federal Deposit Insurance Corp. Chairman Travis Hill, according to Banking Dive.
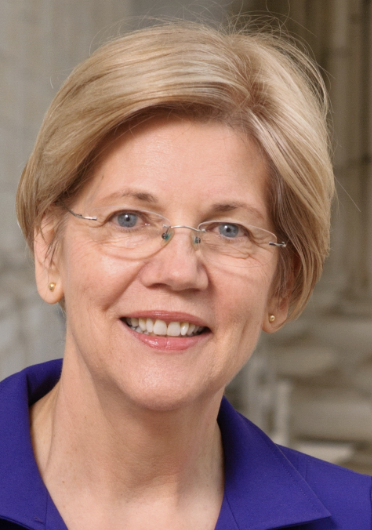
In her letter to Bowman, Warren criticized a September revision to the Federal Reserve’s supervisory operating principles, arguing it sets an excessively high threshold for examiners to flag risks or pursue corrective action. Warren said the policy could constrain intervention when harm is possible, material but not deemed significant, or difficult to quantify.
No Time to ‘Gut’ Protections
“As advancements in frontier AI increasingly enable bad actors to conduct cyberattacks, the Fed should be strengthening bank examiners’ supervisory tools and their ability to enforce strong cybersecurity standards, not gutting them,” Warren wrote, according to Banking Dive.
Warren pointed to a June Texas Bankers Association survey that found 76% of responding banks reported an increase in cybersecurity attacks over the previous year and 84% were increasing cybersecurity investments to address AI-related risks.
In a separate letter to Gould and Hill, Warren challenged an August change to how the Office of the Comptroller of the Currency and FDIC define unsafe or unsound practices for matters requiring attention, a supervisory designation used to identify problems requiring a bank’s response.
What Revised Approach Calls For
Under the revised approach, Warren argued, examiners could act on a cybersecurity vulnerability only when material harm to a bank’s financial condition is likely, rather than merely possible or plausible.
“The narrowed definition of an unsafe or unsound practice means examiners can only take action if it is ‘likely,’ rather than merely ‘possible’ or ‘plausible,’ that a cybersecurity incident could materially harm the financial condition of an institution,” Warren wrote, according to Banking Dive.
Warren said the changes weaken incentives for banks to maintain strong cybersecurity policies, procedures and internal controls. She urged the agencies to rescind the revisions.